Full-stack custody,
built for institutional
operations

The Vault Custody combines secure digital asset infrastructure with the operational tools institutions actually need, built to integrate with the systems you already run, with your assets under your control at every level.

Key sovereignty, configured to your model

Threshold MPC and HSM-anchored key protection, in the configuration you choose: fully managed SaaS, SaaS with a self-hosted signer, or on-premise, where every key and every operation stays inside your perimeter. The cryptography is the same at every level; what changes is how much of your key material and operational data sits inside your own perimeter.

Omnichannel Access

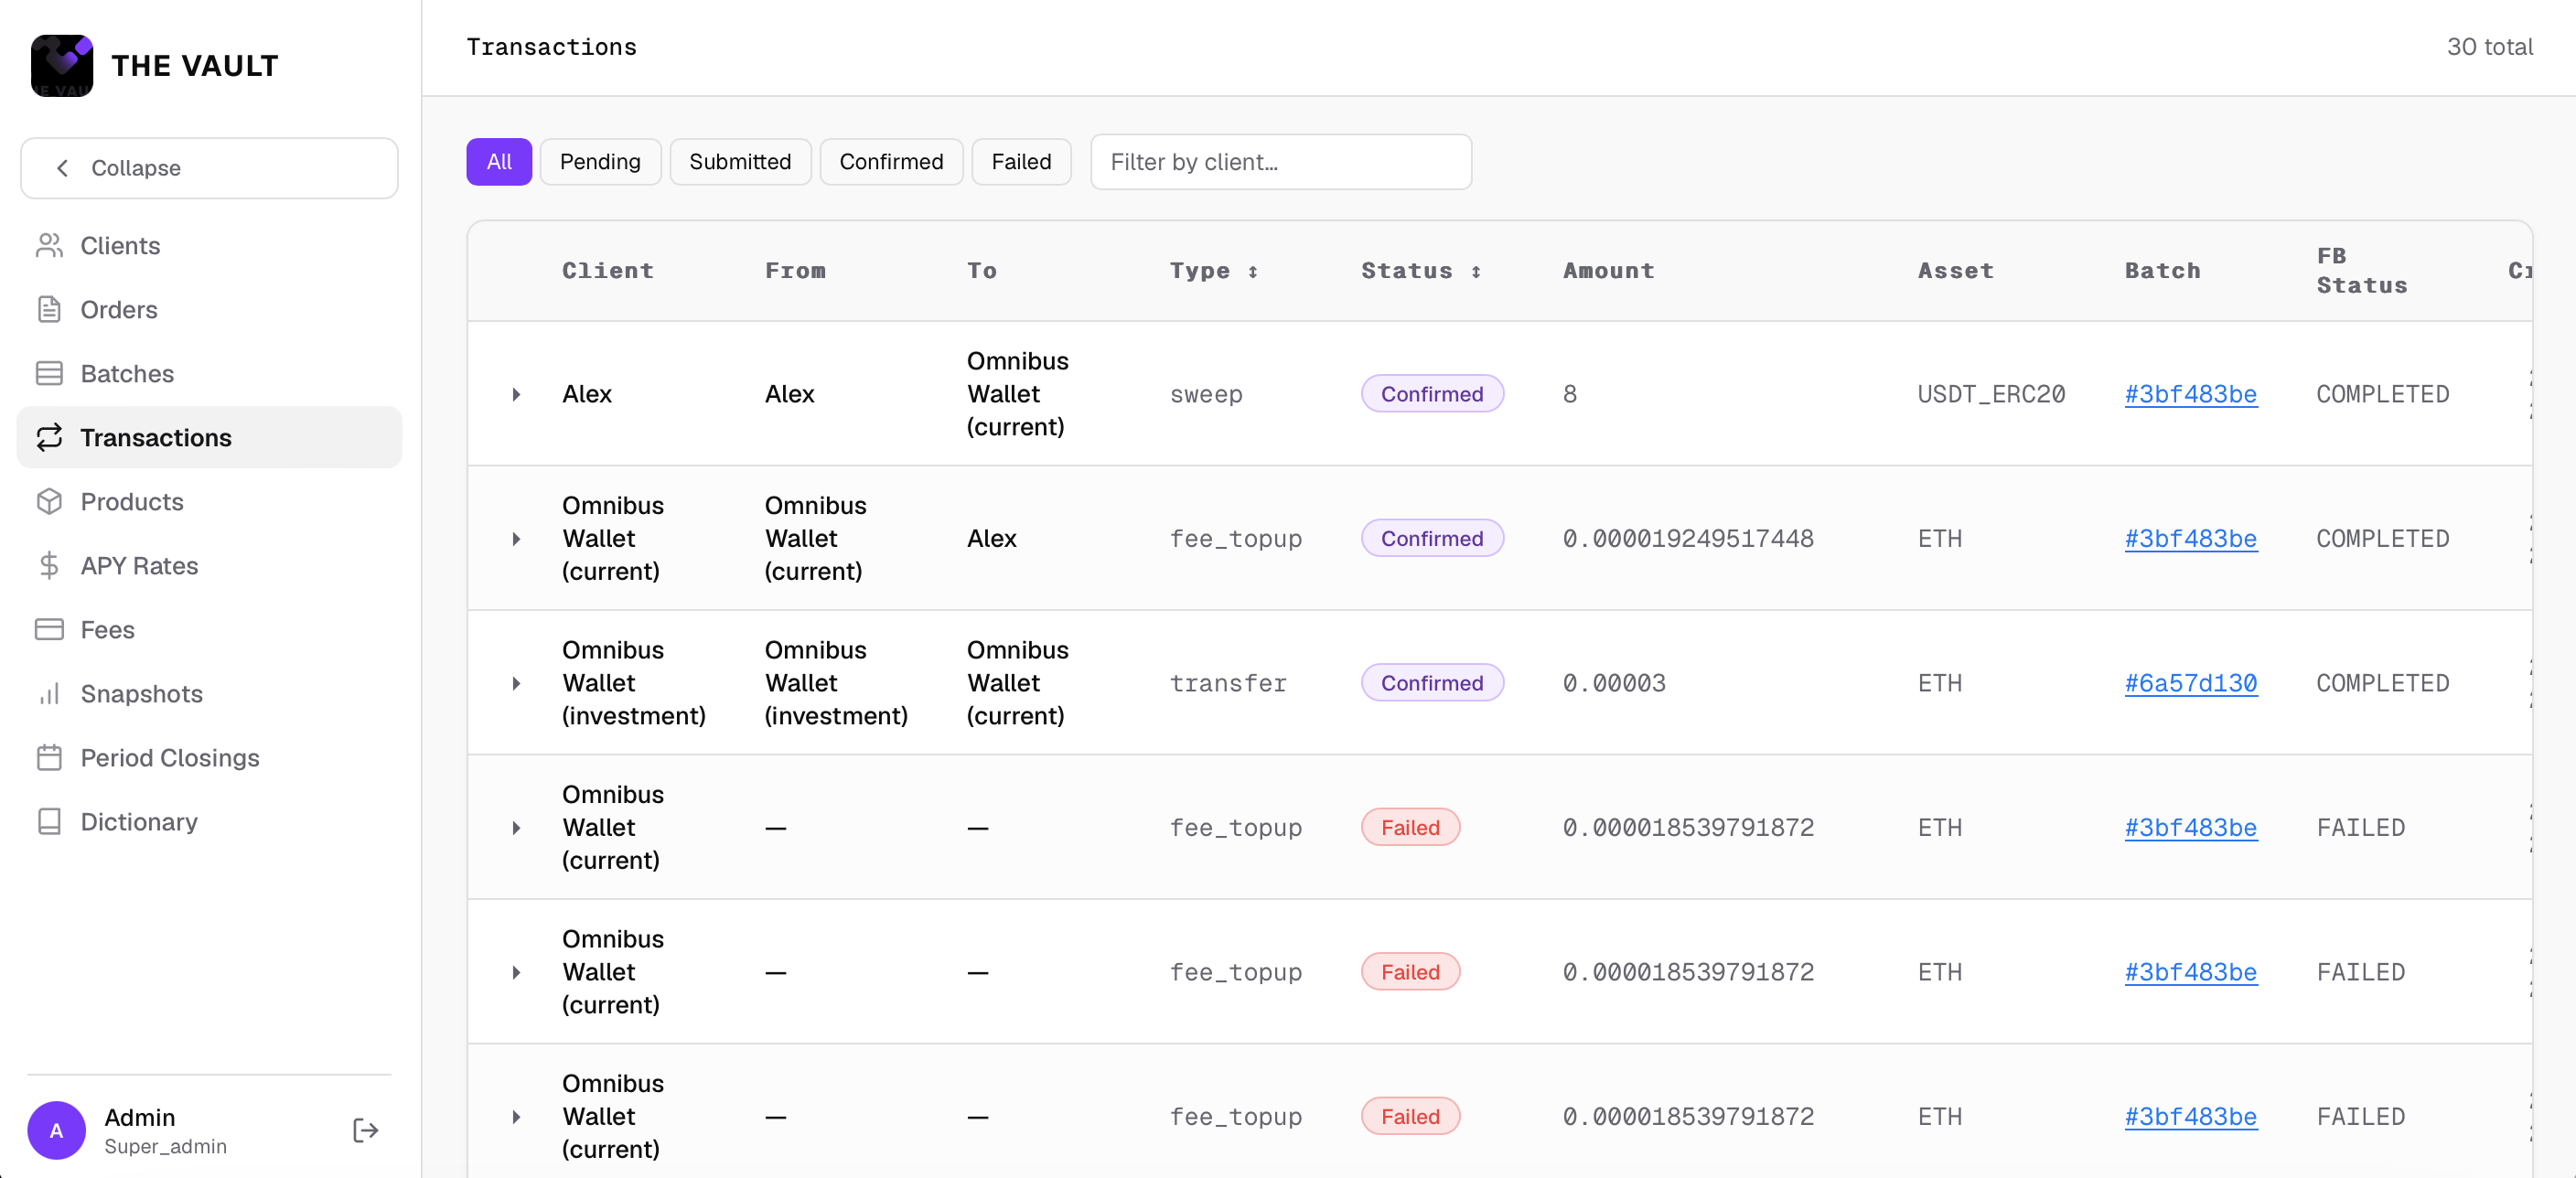
The custody platform runs as a web portal, mobile application, and API, giving your operations, compliance, and treasury teams structured, permissioned access to every wallet and transaction across your infrastructure.

The Vault Custody app, live on

Built for Governance

Multi-wallet management, real-time transaction monitoring, and a robust policy engine that governs every fund movement before it reaches the blockchain.

Two configurations. The same cryptography in both.

SaaS

Runs in
Our environment
Live in
Hours

We run the platform. You create your organisation, configure your policies and start moving assets, usually in hours rather than quarters. There is no infrastructure to procure and no deployment project.

A self-hosted signer is available on top of SaaS, putting a key component inside your perimeter without moving the whole platform.

Read about SaaS

On-premise

Runs in
Your infrastructure
Live in
Weeks

The entire platform runs in your infrastructure, on your hardware or in your own cloud tenancy, under your control. Nothing about the deployment depends on us being available.

Hot, warm or cold key distribution, adjustable per wallet or asset class.

Read about On-premise
Full comparison: SaaS vs On-premise
 SaaSOn-premise
Time to first transaction Hours Weeks
Who runs it day to day We do, fully managed Your team, end to end
Where the platform runs Our cloud Entirely inside your perimeter
Where key shares live Split between our cloud and your devices, never in one place On your infrastructure and your devices, we hold nothing
Who signs transactions You and our co-signer, neither side can move funds alone Only you, every share stays under your control
Who holds operational data We host it You do, inside your perimeter
Team required on your side None A dedicated infrastructure and operations team
Shape of the cost Monthly subscription Capital and headcount
Changing later Move to on-premise Move back to SaaS

Eight controls, enforced before anything moves.

Multiple Wallets

Unlimited wallets and addresses from a single interface.

Role-based Teamwork

Multi-user access with clearly defined roles and permission levels.

Process Automation

Operational workflows, driven from the portal or straight over the API.

Advanced Key Handling

Secure private key generation, storage, and usage with modern cryptography.

System Administration

Centralised user and policy configuration.

Operational Monitoring

Detailed reporting on balances, transactions and approvals.

Transaction Governance

Rule-based approval policies, spending limits, and address whitelists.

Compliance Tools

Counterparty screening for AML support.

Modules, on the same key architecture

  • P2P.org Institutional staking Validator infrastructure, inside custody
  • Hinkal Confidential Wallets An on-chain privacy layer, integrated
  • Finery Markets OTC settlement OTC liquidity, settled from custody

Security architecture & compliance controls

Security and compliance standards
  • Member of VQF Active
  • MiCA · CASP Active
  • SOC 2 Active
  • Security Audit Complete
  • ISO 27001 In progress

MPC and HSM
Key Security

The cryptography is our own. Our in-house research team wrote the threshold MPC library the platform signs with, and Halborn has reviewed it independently, so the security of the platform does not rest on a third-party signing stack we cannot inspect. It is a true T-of-N scheme: no complete private key is ever assembled in a single location, key shares are distributed across client devices and TEE-secured servers, and HSM-anchored protection is available where hardware-backed storage is required.

This architecture eliminates the risk of key theft even in the event of a server breach, a standard that most institutional digital asset custody solutions do not meet.

See security →
Compliance & Governance →

Start where it is fastest, and change it when you know more.

Tell us which configuration you are considering and the level of activity you expect, and you leave the conversation with a figure you can put in next year's budget.

info@thevault.inc